Reporting: cooling incidents in several European countries
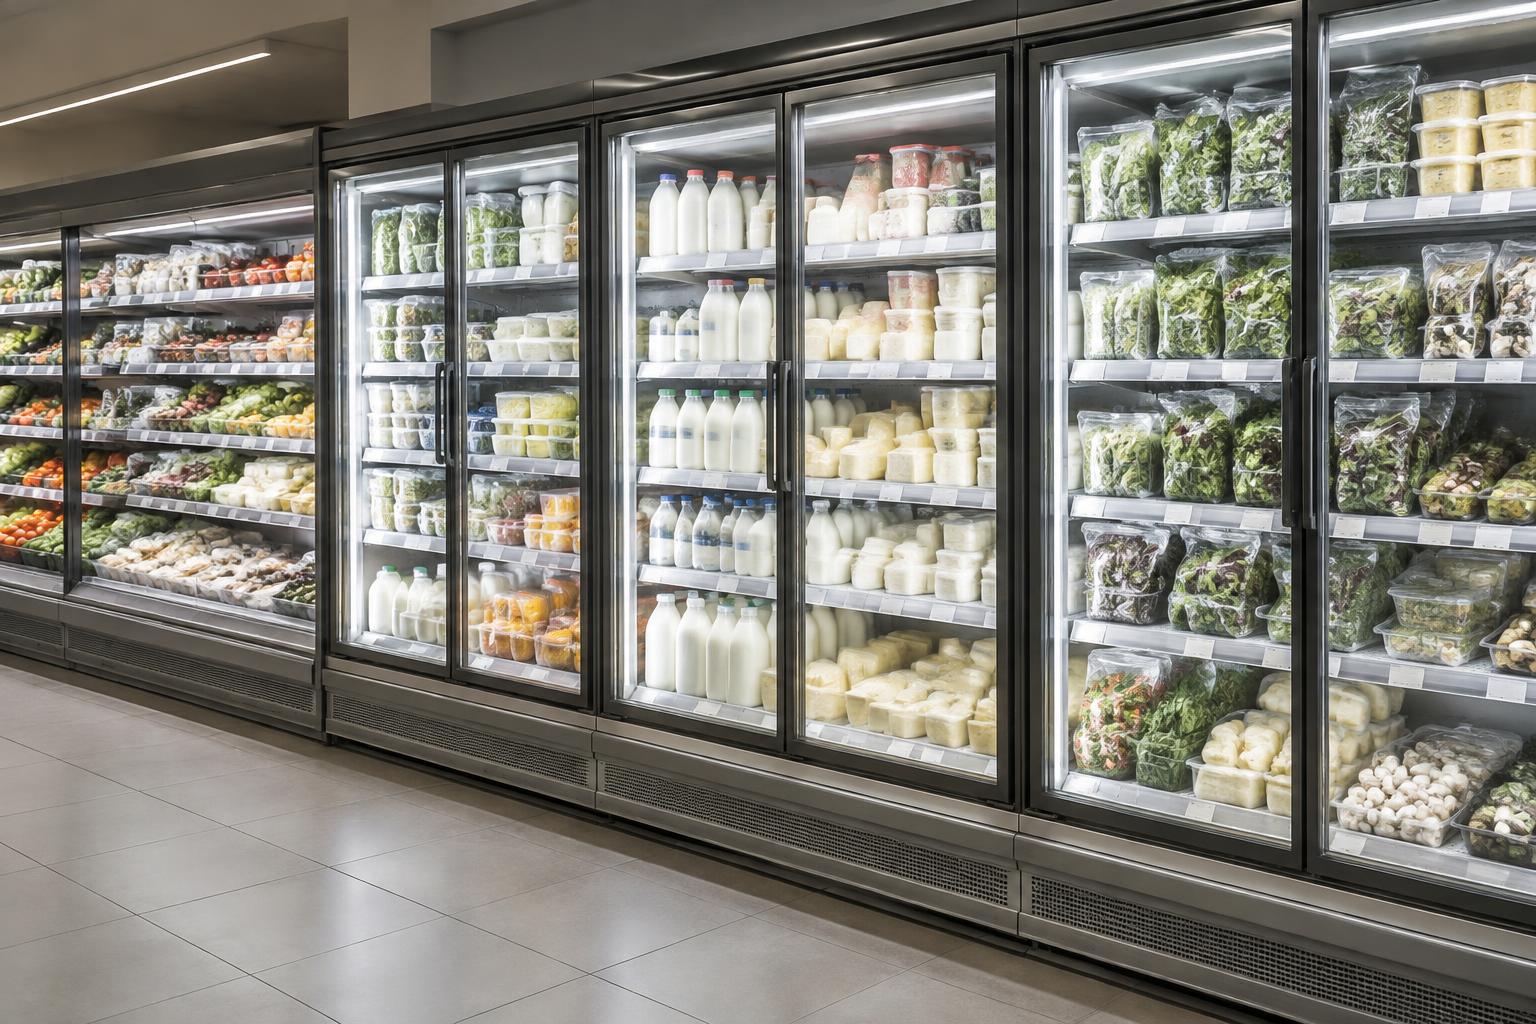
On 2 November, SRF, Reuters and Euronews reported incidents involving supermarket refrigeration and freezer systems. SRF named Belgium, Sweden, Ireland, Luxembourg, Estonia and the Netherlands. The reports describe affected stores and equipment—not all supermarkets in those countries. Available accounts differ in their geographic coverage and in the figures they cite; they should not be combined into a supposedly complete European outage total. [1][2][3]
In Sweden, ICA Kvantum in Sjöbo reported temperatures of up to 50°C in cooling and freezer equipment and attributed the problem to hackers. Reuters and SRF relay that store account; it is not a temperature measured at every affected retailer. Elsewhere, chilled or frozen products were removed from sale as a precaution or spoiled food was discarded. These consequences matter, but the reports do not establish one audited total of damaged stock or financial losses. [1][2][3]
Defrost mode: an attributed account, not a universal explanation
SRF cites refrigeration-services company Sabcobel as saying that systems had been remotely switched into defrost mode. That account helps explain how a legitimate equipment function can have harmful consequences when misused. It does not prove that every reported incident used the same technical path. Nor does it establish how an attacker gained access, which credentials were involved or whether a particular vulnerability was exploited across countries. [1]
Similar refrigeration incidents had already been reported in France in October; SRF refers to around 150 affected shops. Similarity is not proof of a connection. Responsibility and the relationship between the attacks remain publicly unresolved in the cited reporting. These articles are a developing news record, not a completed technical investigation. [1][2][3]
Analysis: the IT/OT boundary is a business boundary
Operational technology controls physical processes. A remote command can change a temperature, a setpoint or an operating state before a conventional IT incident response is complete. The refrigeration cases therefore illustrate why cybersecurity and site operations need a joint response: account misuse can become a stock, safety or availability issue rather than only a data issue.
There are transferable governance questions for PV, BESS and charging infrastructure. Who can act on equipment, what changes are allowed and how is abnormal behaviour detected? This does not mean an inverter, battery controller or charger uses the refrigeration systems’ attack method. Architectures, interfaces and safety mechanisms differ. Huatacondo, discussed in our companion article, raises a separate availability and recovery question—not evidence of the same exploit.
Operator priorities: access, observation and response
A useful review starts with the operating process rather than a product purchase. Agree responsibilities with maintenance providers, map remote interfaces and check whether physical anomalies reach someone empowered to act. System updates need ownership, compatibility assessment and a safe deployment plan; unsupported controls need a replacement strategy. Emergency reaction should be rehearsed with engineering and local staff, including safe restrictions on remote access and verified restoration.
- Are remote privileges assigned to named people, limited to tasks and reviewed regularly?
- Are maintenance sessions approved, recorded and ended when the work is complete?
- Does monitoring cover unexpected settings and physical process values, not just login events?
- Who assesses updates and support expiry for controllers and remote-management systems?
- Can local teams respond safely and restore verified settings if remote control is misused?
No retrospective prevention claim
The practical conclusion is disciplined access management, secure remote maintenance, monitoring, system updates and emergency response. SaiFlow-related links below provide product context for energy-infrastructure discussions, not a claim about the retailers’ systems. Nothing in these reports establishes that SaiFlow would have prevented the attacks or that a single solution removes operational cyber risk.
Sources & further reading
Sources reviewed on 3 November 2026; incident reporting dated 2 November. SRF and Euronews were read directly; Reuters reporting was also checked through syndicated text. Country coverage and attribution differ between reports. Recommendations below are editorial analysis, not forensic findings.