A digital incident with a physical consequence
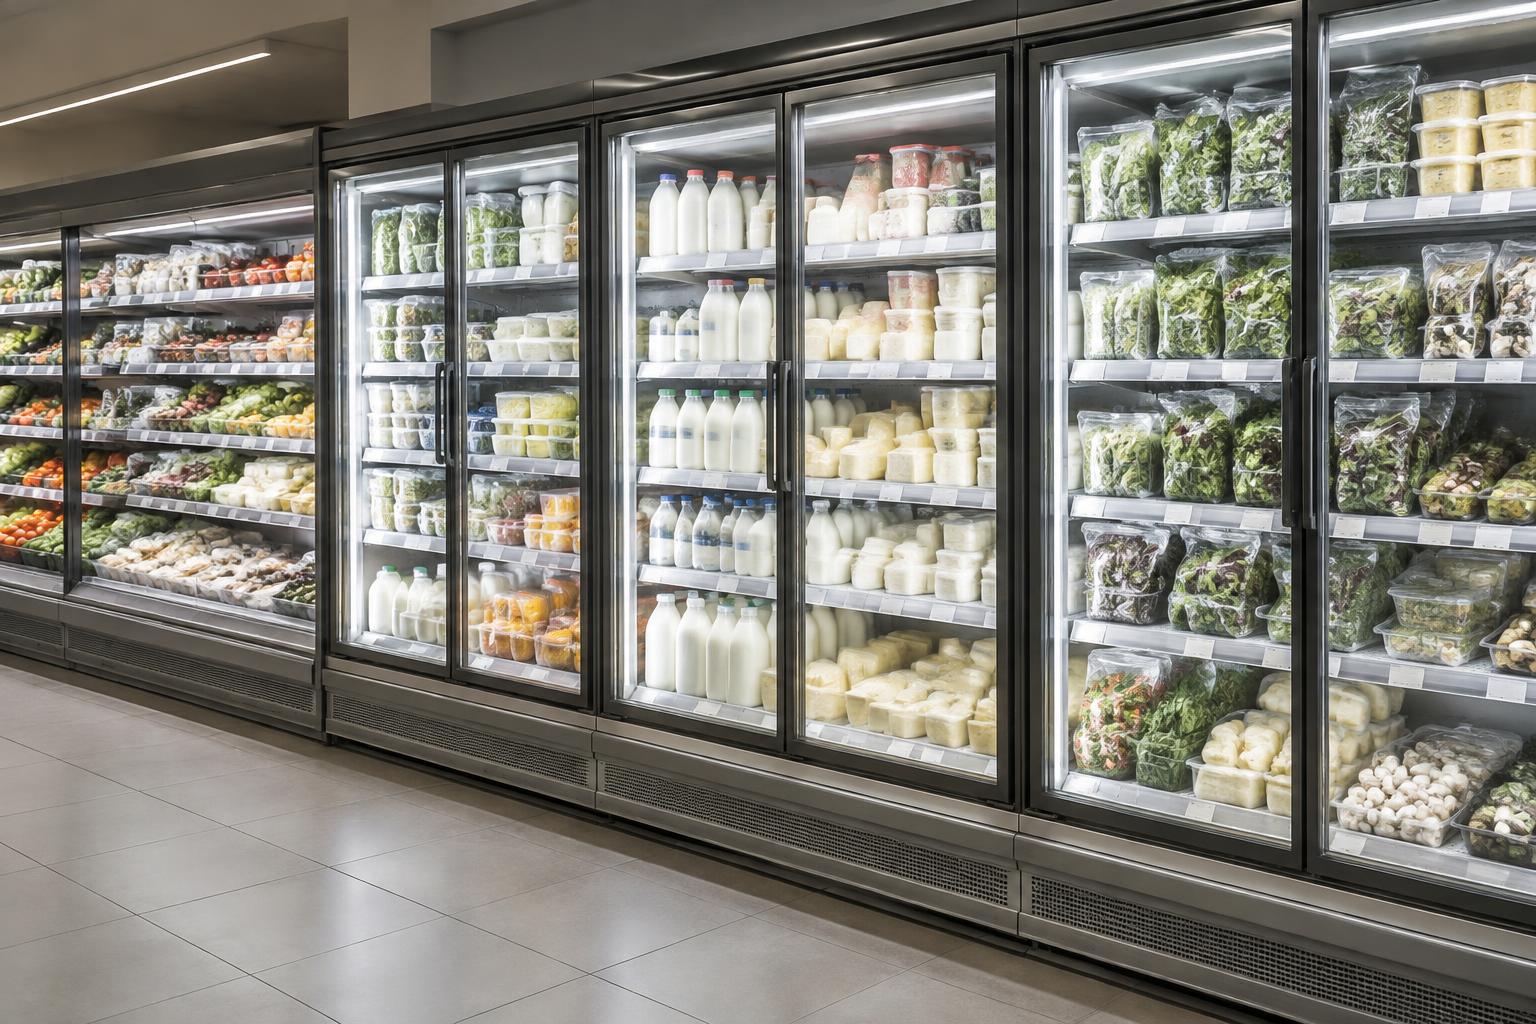
Reporting on 12–13 October 2026 describes cyberattacks that disrupted refrigeration controls at French supermarkets, including Intermarché and Netto, alongside other chains. Reuters reported that refrigerator and freezer temperatures were raised, damaging food; AP described refrigerated displays remaining unavailable and a criminal investigation into spoiled goods and reports of fires. The immediate business problem was not simply an unavailable application. It was the interruption of a temperature-dependent operating process.
Affected-store figures differ between reports and reporting times, so they should not be treated as one settled total. Reuters cited an executive estimate of substantial financial losses, not a final audited amount. The investigation remains ongoing. These reports do not establish a complete, independently verified attack chain, and previously disclosed vulnerabilities should not automatically be presented as the confirmed route into these incidents.
Why legacy remote control is a business continuity risk
SRF’s 13 October report describes around 150 affected French shops and refrigeration temperatures reaching approximately 50°C. It cites Bernhard Egger, head of the Information and Cybersecurity degree programme at Lucerne University of Applied Sciences and Arts, on risks from ageing software, insufficient updates and centrally connected remote control, compounded by limited local IT expertise. These are attributed expert observations, not proof of the precise attack vector. For operators, the continuity question is who maintains legacy controls and can intervene when central access is misused; neither universal device vulnerability nor prevention by a particular product follows from this report.
The lesson for distributed infrastructure
Refrigeration is operational technology: digital commands affect physical equipment and operating conditions. Remote management helps maintenance teams supervise dispersed sites, but it also makes access arrangements commercially significant. A change to a control setting can affect stock, service availability and recovery costs before a conventional IT investigation is complete.
Charging, storage and distributed energy operators should recognise the pattern without assuming identical vulnerabilities. Their assets have different architectures and safety protections. Nevertheless, remotely accessible controls, shared service accounts and centrally managed fleets deserve attention because the consequences of misuse extend beyond lost data. A maintenance pathway is part of the operating model, not merely a convenient technical feature.
Business continuity therefore needs to connect cybersecurity, engineering and site operations. Network segmentation can limit pathways between business systems and operational controls, but only if the actual connections and permitted traffic are understood. Access oversight must include external service providers. Monitoring should make unexpected settings and physical behaviour visible to people who can respond, rather than relying exclusively on evidence that someone logged in.
Questions to put to operations and suppliers
Use the incident as a prompt for a focused review—not as proof that your equipment is vulnerable. Ask for documented answers and exercise recovery arrangements with the people responsible for the site:
- Which systems can change operational settings, and are any management interfaces reachable directly from the internet?
- Who has remote access, through which identities and devices, and who approves, records and revokes each maintenance session?
- Where are operational networks separated from office IT and supplier connections, and how is that separation checked?
- Who owns firmware support, patch assessment and replacement planning for legacy controllers?
- Can operators detect abnormal settings independently, restrict remote control safely and restore a verified configuration without losing essential operations?
From awareness to a defined scope
POWERbuilder Protect offers a starting point for discussing infrastructure risk with specialist providers. SaiFlow Security and Secure Remote Access address distinct questions around energy-contextual cybersecurity and controlled maintenance access. Their suitability must be assessed against the equipment, interfaces and responsibilities of each project. Neither this incident nor a product description establishes that a particular solution would have prevented the French attacks. The practical objective is clearer visibility, accountable access and a recovery plan grounded in the real operating environment.
Sources & further reading
Reporting and research checked on 13 October 2026. Operational recommendations are POWERbuilder Intelligence’s editorial analysis.