Research, not a reported Swiss blackout
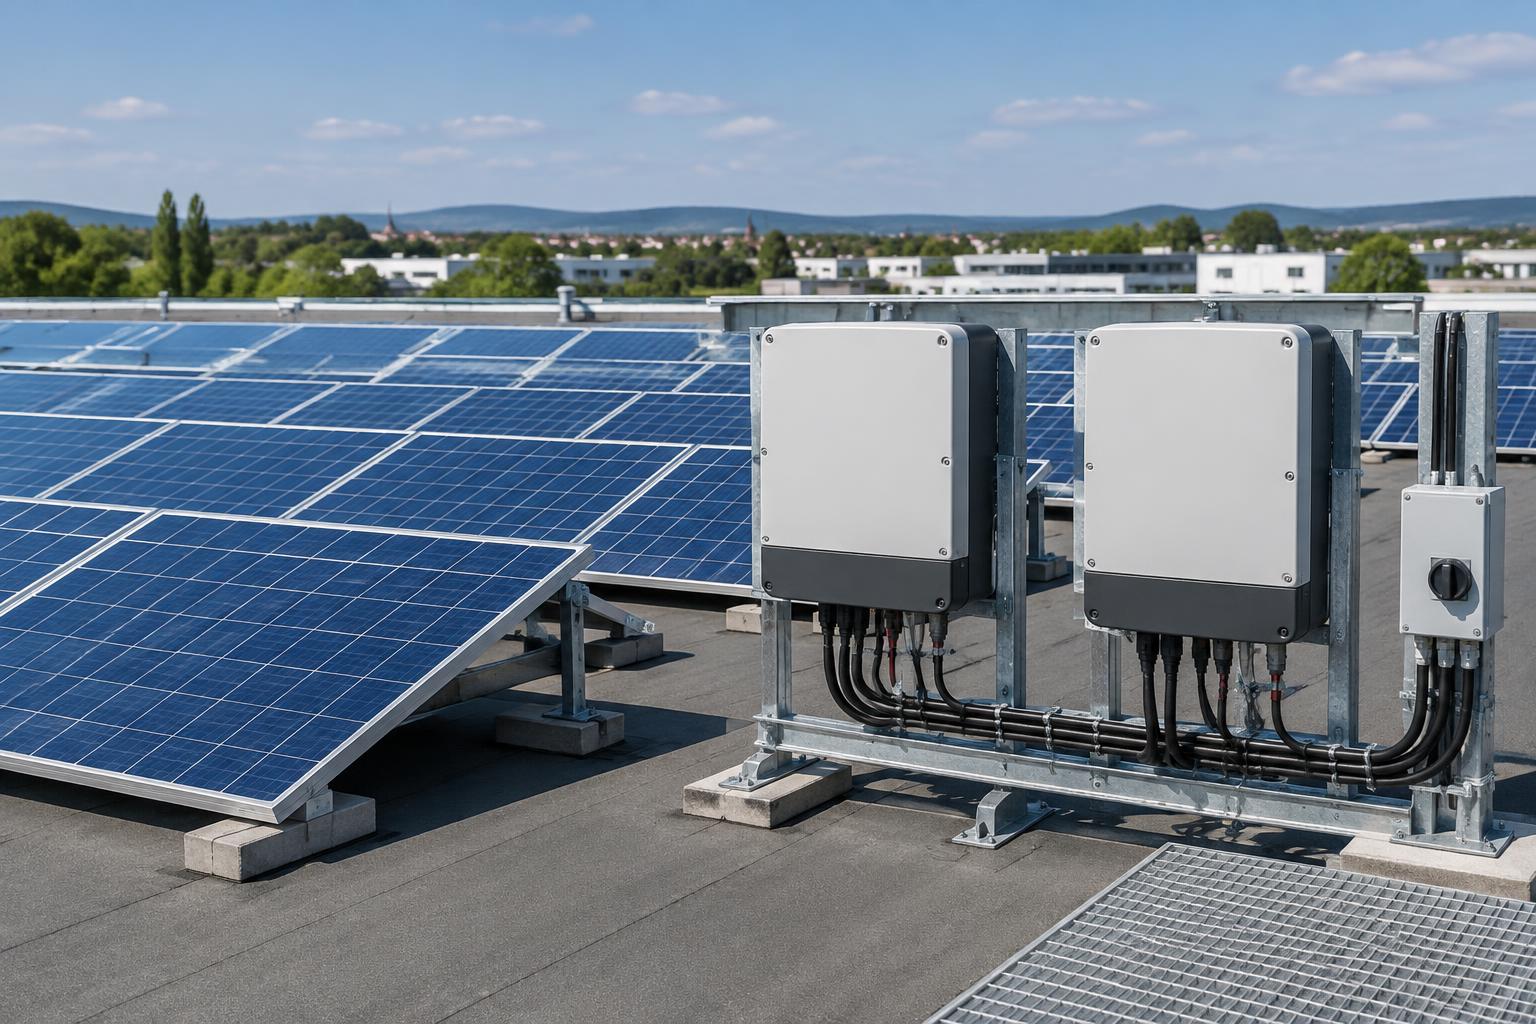
On 17 September 2026, SWI swissinfo.ch published reporting based on SRF coverage of research by the National Test Institute for Cybersecurity, NTC. The article describes cybersecurity weaknesses in connected solar systems and a broader concern: remote access to many inverters could turn dispersed installations into a concentrated operational risk. Swissinfo reports more than 338,000 photovoltaic installations in Switzerland. That scale makes the governance of connected equipment relevant beyond any individual rooftop.
The distinction matters: this is research into vulnerabilities and potential coordinated disruption, not a report of an actual Switzerland-wide blackout caused by solar inverters. NTC examined inverters and energy-management systems and reported weaknesses affecting control of equipment. Its findings also highlight a structural issue: thousands of installations connected to a small number of manufacturer clouds. Fixing individual product flaws and managing fleet-level dependencies are related, but different, tasks.
Remote connectivity changes the control boundary
An inverter converts electrical power, but its digital interfaces can also enable monitoring, configuration and operational changes. Manufacturer-cloud connectivity offers useful support and visibility. It also introduces questions about which parties can influence equipment, what authority they hold and how that authority is constrained. Ownership of the physical installation does not, by itself, describe every remote control relationship.
The grid-risk argument depends on scale and coordination. One installation going offline is not equivalent to a fleet changing output at the same time. Swissinfo describes expert concern that simultaneous interference with a large group of devices could threaten grid stability. The outcome would depend on operating conditions, affected capacity and system responses. It is not a prediction that every connected inverter will cause an outage, nor evidence of malicious intent by a specific manufacturer.
For distributed energy and charging operators, the useful lesson is to examine dependencies across sites. A common cloud, integrator account or maintenance arrangement can create a shared control boundary even where assets are geographically dispersed. Reviews should consider both the equipment and the services connecting it. Technical diversity alone does not resolve identity management, unsupported firmware or unclear responsibilities.
A practical procurement and operations checklist
Before expanding a fleet or renewing a service arrangement, bring engineering, IT security, procurement and the relevant suppliers into the same discussion. Ask for evidence rather than general assurances:
- Which local and cloud interfaces can change output, configuration or firmware, and which organisations control those interfaces?
- What proportion of the fleet depends on one cloud service, supplier account or remote-management platform?
- Can access be limited to named identities, approved tasks and defined time windows, with usable records of changes?
- What happens if cloud connectivity is lost or deliberately restricted, and has safe local operation been tested?
- Who tracks security advisories, manages updates and support expiry, and verifies restoration of approved settings?
Make the operating relationship explicit
The goal is not to abandon connected solar or imply that one nationality or brand determines security. It is to make control, concentration and recovery responsibilities explicit. POWERbuilder Protect provides a route to specialist assessment; SaiFlow Security and Secure Remote Access can be discussed where energy-contextual visibility or controlled servicing is relevant. Supported equipment and provider scope require individual confirmation. No product can be credited here with preventing a hypothetical coordinated grid event. A defensible first step is knowing who can act on your infrastructure—and how you would respond if that authority were misused.
Sources & further reading
Reporting and research checked on 13 October 2026. Operational recommendations are POWERbuilder Intelligence’s editorial analysis.